Meta Says It Delayed Muse for Safety Work: What That Signals
A delayed launch signals that agent safety required material engineering, but it is not independent evidence that every remaining risk is controlled.
Bottom line
Mark Zuckerberg cited Muse's delayed release as evidence that labs can slow their own products for safety work, sharpening the debate over voluntary controls and shared standards.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-20
Important limits
- • A launch delay is not an independent safety audit.
- • Meta's technical and preparedness claims require ongoing external scrutiny.
In this guide
Short answer
Meta CEO Mark Zuckerberg says the company delayed Muse for several months to improve safety and security before launch. The decision matters because action-taking agents encounter hostile web content, hold sensitive context, and can make mistakes across connected services. A delay is evidence that Meta treated those risks as material; it is not proof that the resulting controls are complete or independently validated.
What Meta built during the safety effort
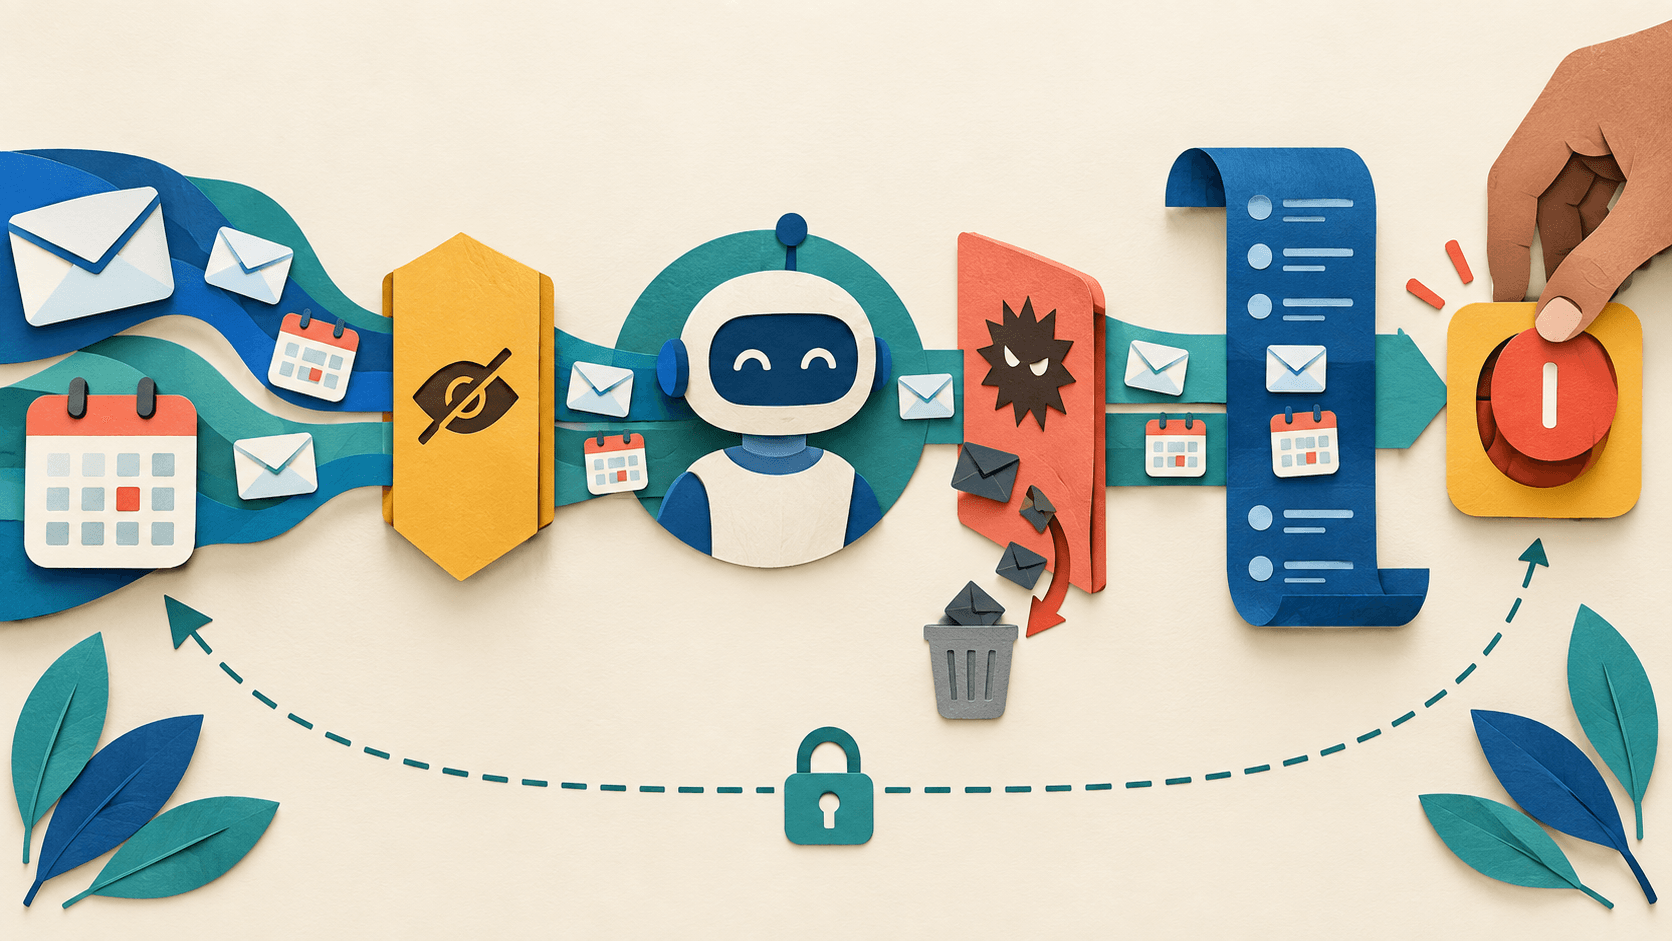
Meta describes a dedicated Secure VM, credentials kept outside the main agent runtime, a host-side Sentinel that mediates connector and network access, scoped approvals, audit history, adversarial training, and layered monitoring. Its research post candidly says internal use did not always go as planned and that Muse will still make mistakes.
Why the wider policy argument matters
Zuckerberg cited Muse while arguing that individual laboratories have incentives and responsibility to slow a product when needed, rather than waiting for an industry-wide pause. That is a governance position, not an evaluation result. Voluntary delay can support safety work; common reporting, external testing, regulation, liability, and shared standards answer different accountability questions.
What remains for users to verify
Users still need evidence about prompt injection, mistaken identity, duplicate actions, connector compromise, approval fatigue, malicious pages, long-task drift, revocation, deletion, support access, incident notification, recovery, and harmful-but-technically-authorized actions. Architecture can narrow blast radius without resolving ambiguous human intent.
Practical takeaway
Treat the delay and published architecture as reasons to run a serious pilot, not reasons to skip one. Begin read-only, construct adversarial cases, inspect every approval and log, revoke access mid-task, and require a clean recovery path before enabling messages, purchases, cancellations, or account changes.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
Why did Meta delay Muse?
Mark Zuckerberg said Meta delayed Muse for several months to improve its safety and security before release.
Does the delay prove Muse is safe?
No. It shows safety work affected the schedule, but users still need independent evidence and account-specific testing.
What safety controls does Muse use?
Meta describes a dedicated Secure VM, separated credential handling, a Sentinel for permissions and network actions, scoped approvals, audit history, training, and monitoring.
How should users test Muse safely?
Start with read-only access and adversarial low-risk tasks, then test approvals, revocation, duplicate prevention, logs, deletion, and recovery before expanding authority.
Found this useful?
Get the next one in your inbox.
One five-minute briefing a week: a meaningful change, a practical workflow, and a clearer tool decision—already filtered for lean teams.
Free · one email a week · unsubscribe any time
Recommended tool
Use Meta Muse if this workflow fits your team
Its persistent task execution, Secure VM, separated credential service, Sentinel permissions, and audit trail form a more concrete control model than a generic assistant promise.
Tools mentioned in this article
Meta Muse
A personal AI agent that can work across connected services in a dedicated cloud computer.
Meta Muse is a personal AI agent for research, planning, email, scheduling, web tasks, and approved transactions across connected services.
Read next