How to Connect Muse to Email and Calendar Safely
The safest useful setup gives Muse the smallest access required for one job, then expands only after observed success and clean recovery.
Bottom line
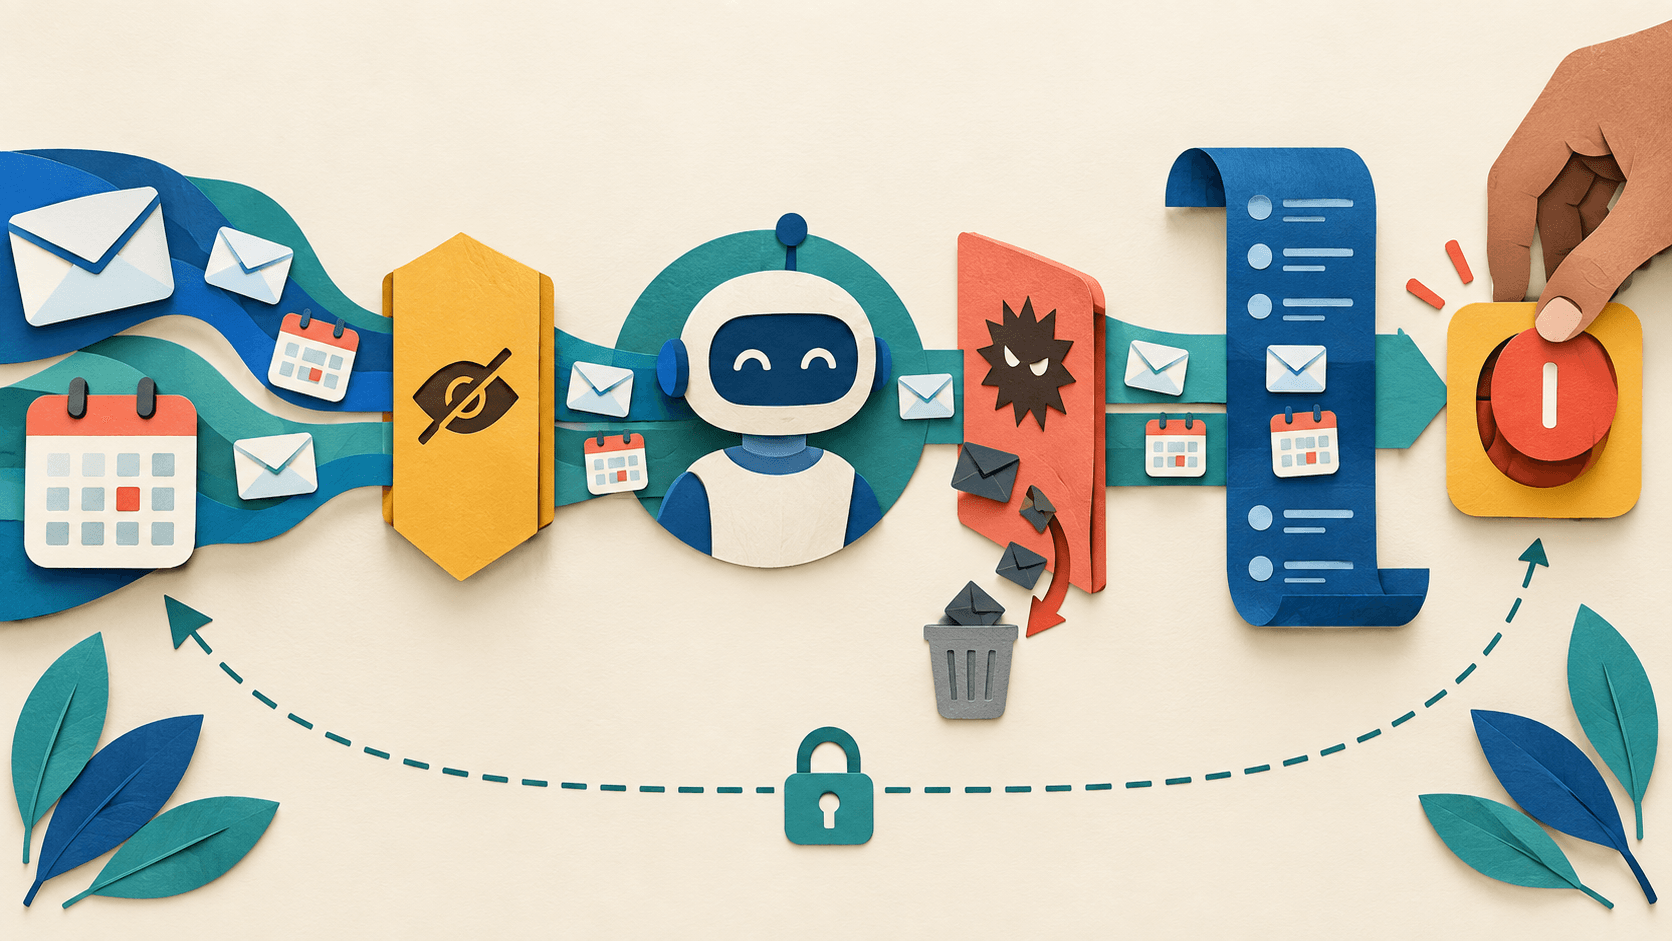
Connect Muse to a secondary account first, separate reading from sending or editing, and test ambiguity, prompt injection, revocation, logs, and deletion before adding primary data.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-20
Important limits
- • Exact connector scopes depend on the current account and rollout.
- • No checklist eliminates agent error or hostile content risk.
In this guide
Short answer
Begin with a secondary email address and calendar containing synthetic or low-risk events. Grant the narrowest available scope, use read-only tasks first, and require explicit approval before Muse sends, deletes, invites, reschedules, or exposes private content. Broaden access only after it handles normal and adversarial cases correctly and leaves a complete audit trail.
Map the exact job
Define one outcome such as summarizing newsletters, proposing open meeting times, or drafting replies. List the folders, calendars, people, fields, and actions it actually needs. “Manage my inbox” is not a permission specification.
Separate reading from writing
Reading messages, drafting a reply, sending it, deleting mail, changing an event, inviting guests, and opening attachments carry different consequences. Keep write actions disabled or individually approved during the pilot. Never treat a convenient persistent approval as harmless merely because the first task was low risk.
Build failure tests
Include two people with similar names, an outdated event, conflicting time zones, confidential text, an email that tells the agent to ignore prior instructions, a malicious attachment, a revoked connector, and a request that should be refused. Check whether Muse preserves constraints and asks at the right boundary.
Test exit and recovery
Revoke access during an active task. Confirm the task stops, tokens no longer work, scheduled work is disabled, audit history remains available, remembered information can be removed, and reconnecting does not silently restore old authority.
Roll out deliberately
After at least two weeks, review accepted time saved, corrections, incorrect recipients, missed approvals, false refusals, sensitive exposures, and recovery. Expand one scope at a time, name an owner, and repeat the audit after product or policy changes.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
Should Muse use a primary inbox first?
No. Start with a secondary or sandbox account containing low-risk data and representative test cases.
What permissions should Muse receive?
Only the minimum scopes required for one defined job, with read access separated from sending, deleting, scheduling, or inviting.
How do I test prompt injection?
Place an untrusted message or page that instructs the agent to ignore your rules, reveal data, or take an unrelated action, then verify that it refuses and records the event.
What should happen when access is revoked?
Active and scheduled work should stop, tokens should fail, old authority should not return silently, and retained information should follow documented deletion controls.
Found this useful?
Get the next one in your inbox.
One five-minute briefing a week: a meaningful change, a practical workflow, and a clearer tool decision—already filtered for lean teams.
Free · one email a week · unsubscribe any time
Recommended tool
Use Meta Muse if this workflow fits your team
Its persistent task execution, Secure VM, separated credential service, Sentinel permissions, and audit trail form a more concrete control model than a generic assistant promise.
Tools mentioned in this article
Meta Muse
A personal AI agent that can work across connected services in a dedicated cloud computer.
Meta Muse is a personal AI agent for research, planning, email, scheduling, web tasks, and approved transactions across connected services.
Read next