In this guide
Short answer
Google says its internal PageBreak security agent found more than 500 cross-site scripting vulnerabilities across first-party web applications while producing a near-zero false-positive rate. The differentiator is a proof-first workflow: models propose attack paths, but specialized non-AI validators execute controlled payloads against running environments before a finding reaches a product team. That pattern could make AI security scanning more useful, though PageBreak is not a public product and Google's internal access gives it advantages most teams cannot reproduce.
Free AI tool buyer checklist
Make the next AI subscription earn its place.
Get the weekly top 5 AI tools, one practical workflow and one way to reduce AI spending. Includes a free buyer checklist.
What PageBreak does differently
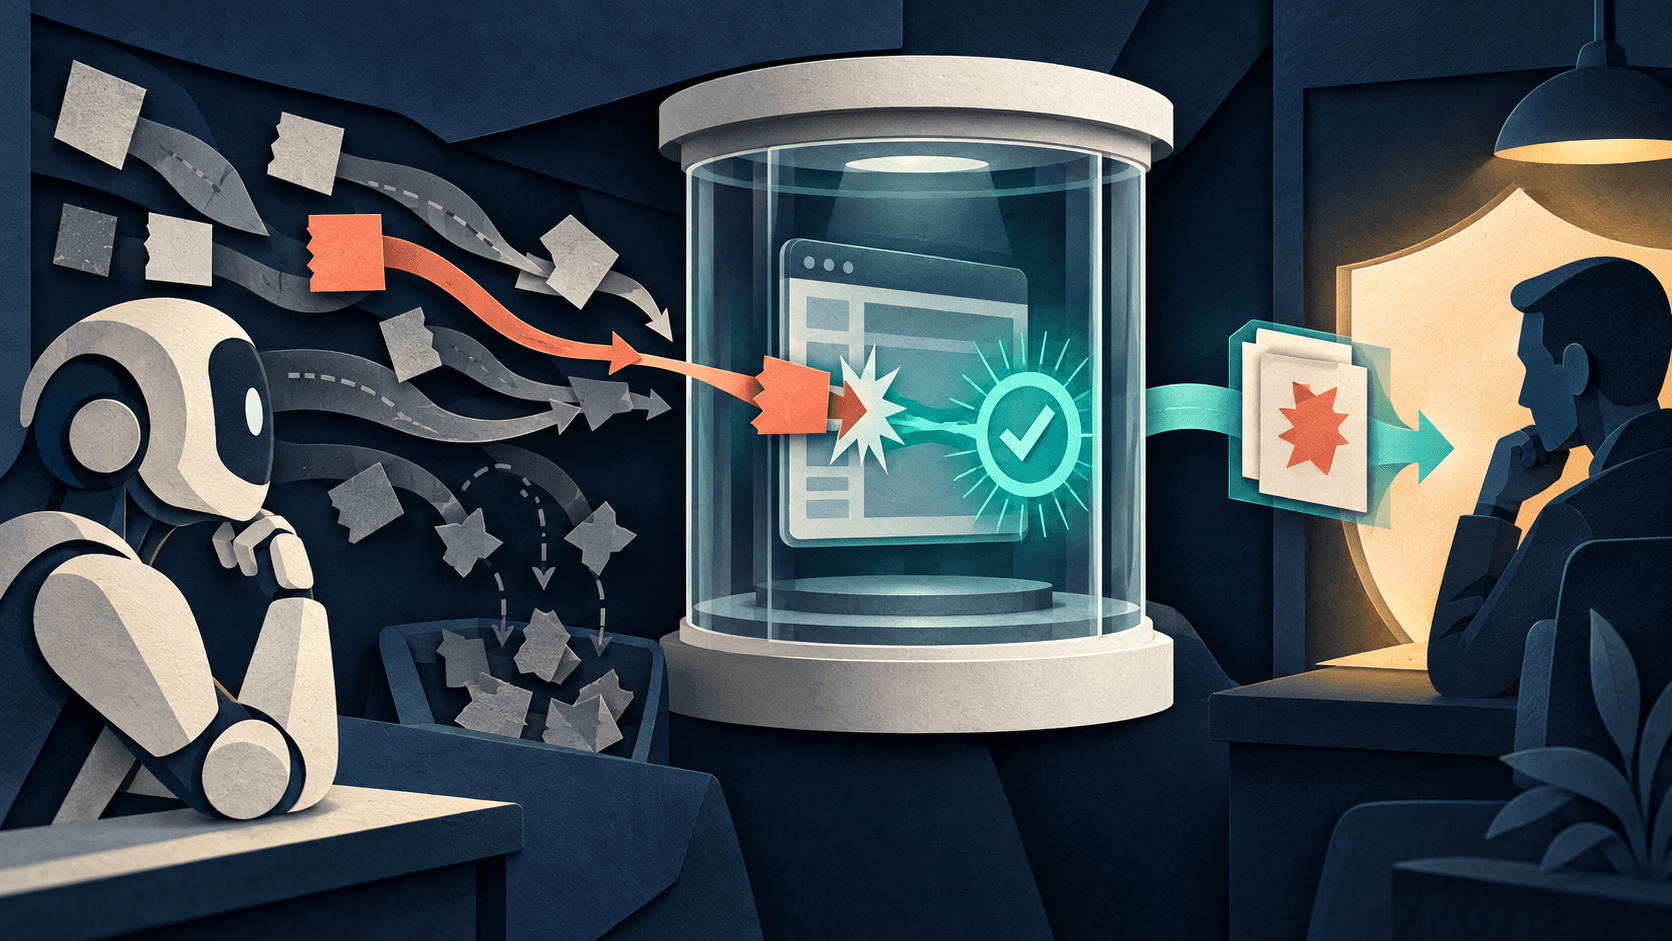
Many AI scanners stop after generating a plausible code explanation. PageBreak tries to close the loop. Its validators check whether JavaScript executes, database behavior changes, a protected file can be read, code execution produces an observable effect, or a server makes an unintended request. An alert is promoted only when the system can produce concrete exploit evidence.
Why deterministic validation matters
Security teams pay for false positives twice: first in triage time and again when noisy tools lose developer trust. A validator converts a model's hypothesis into a repeatable test with an explicit pass or fail condition. It also creates a stronger handoff artifact—affected path, payload, observed result, and reproduction environment—than a fluent explanation alone.
How Google handles findings it cannot prove
PageBreak still retains nondeterministic candidates, but Google says it does not send them to product teams. Instead, those candidates seed later investigations, reveal missing environment access, and help engineers decide which new validators to build. This creates a disciplined backlog without presenting unverified model output as a confirmed vulnerability.
The reported results and their boundary
Google reports more than 500 XSS discoveries and near-zero false positives, but it has not published the denominator, recall, severity distribution, duplicate rate, review cost, or independent reproduction rate. A proof-only queue can also miss flaws when no validator exists. Low false positives therefore do not establish high coverage.
Google's structural advantage
PageBreak can traverse Google's monorepo, map live traffic to source, authenticate to internal applications, and reuse mature scanning infrastructure. Those privileges help it follow vulnerabilities across services and verify behavior in realistic environments. A company with fragmented repositories, incomplete test environments, or weak asset identity should not assume the same results from the same model.
The opportunity for security teams
The transferable idea is to fund validators before buying more detection volume. Start with a narrow vulnerability class and a disposable, production-like environment. Require an executable proof, capture every side effect, separate confirmed findings from research leads, and measure analyst minutes per accepted vulnerability. Keep destructive payloads, credentials, and network egress bounded.
A safe evaluation plan
Seed known vulnerabilities and hard negatives in an isolated application. Measure recall, confirmed precision, time to proof, duplicate findings, validator coverage, unsafe actions, compute cost, reviewer effort, and patch acceptance. Run conventional scanners in parallel. Do not give an experimental agent unrestricted production credentials merely because it is designed to find security defects.
Bottom line
PageBreak's real contribution is an operating principle: AI-generated security claims should earn trust through executable evidence. The approach can reduce noise and improve prioritization, but organizations still need isolation, least privilege, human review, recall measurement, and secure remediation.
Transparency
How this guide was checked
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 2
- Last checked
- 2026-09-24
Important limits
- • Reported results come from Google and are not independent proof of general production outcomes.
- • Timelines, architecture, performance, and availability can change as these projects develop.
Sources and references
References cited by this article. Check the original source for scope, dates and current terms.
Frequently asked questions
What is Google PageBreak?
PageBreak is an internal Google Product Security agent that searches first-party web applications for vulnerabilities and uses specialized validators to confirm exploitability.
How does PageBreak reduce false positives?
It executes controlled proofs against running environments and promotes a finding only when a validator observes the expected exploit behavior. Unverified candidates stay out of product-team queues.
Is PageBreak available to other companies?
Google describes PageBreak as an internal project, not a generally available product. Its design principles can inform other programs, while CodeMender is a separate Google Cloud remediation offering in preview.
Does near-zero false positives mean PageBreak finds every flaw?
No. Precision and recall are different. A strict validator can keep alerts accurate while missing vulnerabilities for which it lacks access, coverage, or a reliable proof method.
Recommended tool
Use Google Gemini if this workflow fits your team
It has one of the clearest workflow fits in its category and is easier to recommend than tools that only look impressive in demos.
Tools mentioned in this article
Google Gemini
Google's deeply integrated AI assistant with unmatched access to Google's ecosystem
Gemini combines powerful AI with Google's vast data ecosystem — Search, Gmail, Docs, YouTube, and more — for a uniquely integrated experience.
Read next