ChatGPT Adds Security History—Here’s What Account Owners Should Review
The new event history makes account changes easier to inspect, but it does not replace strong authentication, offboarding, workspace controls, or an incident plan.
Bottom line
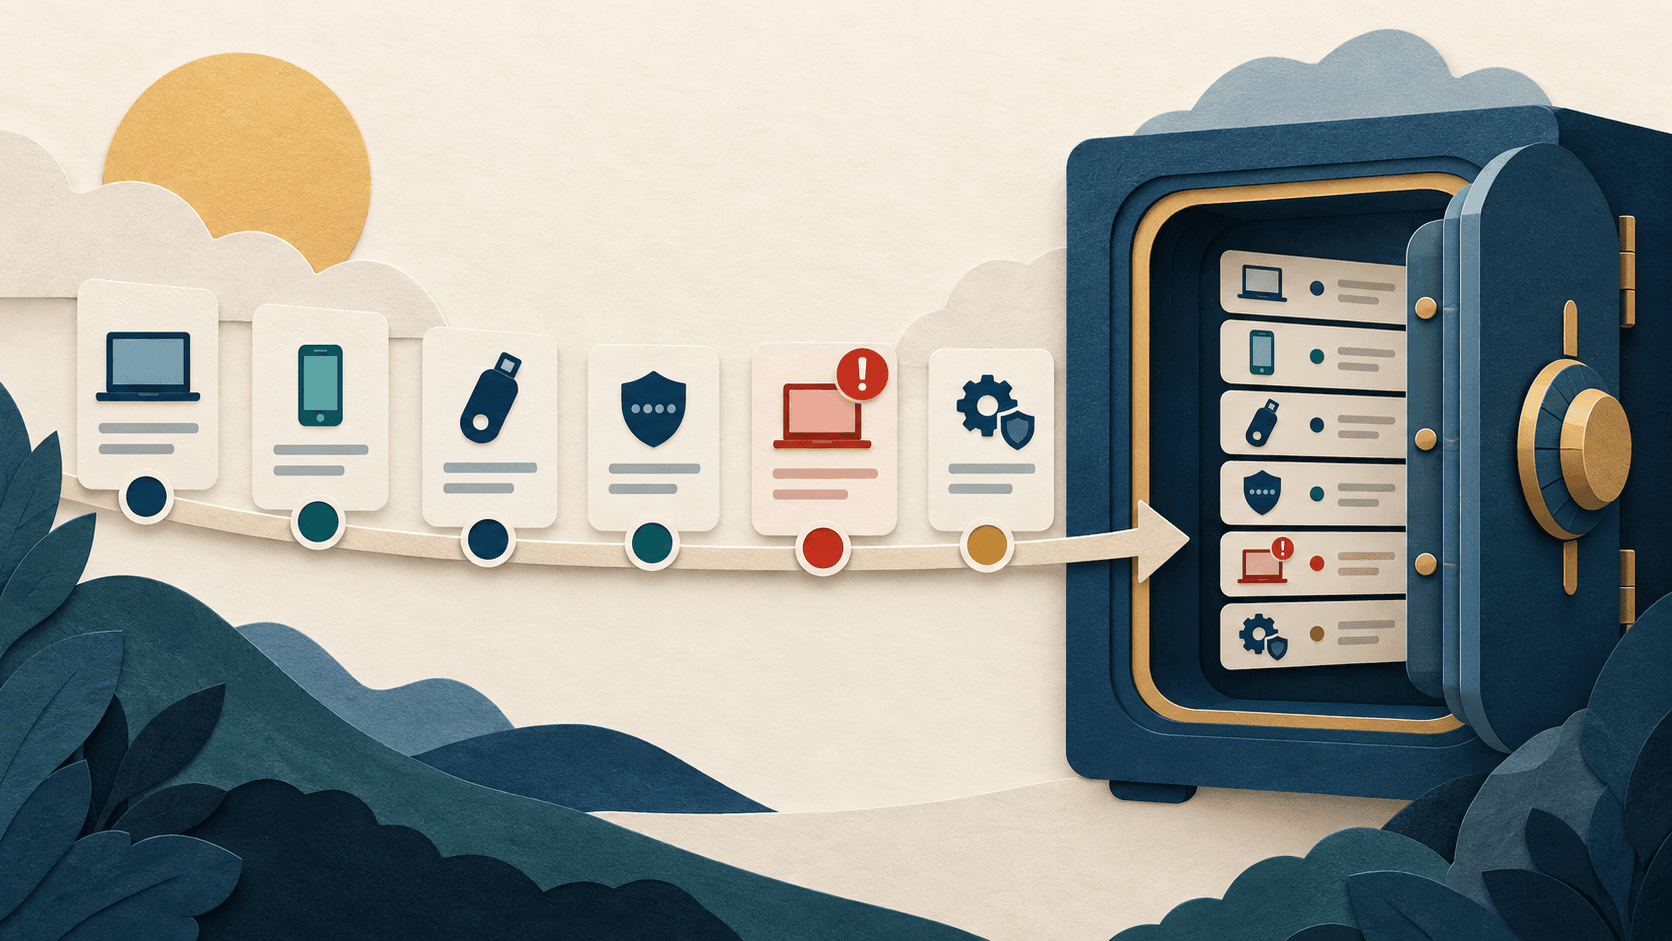
ChatGPT's new Security History shows sign-ins, devices, MFA, passkey, and security-setting changes. Review it now and document how your team handles unfamiliar activity.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-27
Important limits
- • Device and location details can be approximate or unavailable.
- • The feature is not a substitute for workspace audit logs, connected-app review, or incident response.
In this guide
What changed
OpenAI added Security History to ChatGPT on September 25, 2026. In ChatGPT on the web, account owners can open Settings → Security and login → Security history to review recent sign-ins, sign-outs, and changes to multi-factor authentication, passkeys, and other security settings. Events can include time, approximate location, and device details.
This is a useful visibility improvement. It is not proof that an account is safe, and OpenAI notes that some location or device details may be approximate or unavailable.
Why this matters for small organizations
Solopreneurs, small businesses, and nonprofits often adopt an AI account before they establish formal identity operations. The account may later contain uploaded contracts, donor material, customer notes, internal prompts, connected apps, or reusable agents. A security history turns some invisible account changes into events an owner can review.
The feature is most valuable when someone is responsible for checking it and knows what to do next. A list of unfamiliar activity without a response procedure is only a better alarm.
A 10-minute account review
- Open Security History from ChatGPT's web settings.
- Match recent sign-ins and devices against your actual use.
- Review changes to MFA, passkeys, recovery methods, and other security settings.
- If anything is unfamiliar, change the password from a trusted device and use the account's sign-out controls.
- Enable MFA or a passkey if the account does not already use strong authentication.
- Review connected apps, shared projects, custom agents, API keys, and workspace members separately; the event history is not a complete asset inventory.
- Record who owns recovery and offboarding for any shared business workflow.
What the feature does not solve
Security History does not make shared credentials acceptable, validate every connected service, revoke old API keys automatically, classify sensitive uploads, or replace workspace administrator logs. Consumer and organizational accounts can also have different controls. Teams should verify the features available on their plan rather than assuming one personal-account screen represents the whole workspace.
If you see unfamiliar activity
Use a trusted device, preserve the visible event details, secure the email account tied to ChatGPT, change reused passwords elsewhere, review MFA and passkeys, remove unknown sessions or connections, rotate exposed API keys, and contact official support. If business or personal data may have been accessed, follow the organization's incident and notification process rather than quietly restoring access and moving on.
Bottom line
ChatGPT Security History is a worthwhile, low-friction control because it gives account owners a place to inspect changes that previously could be easy to miss. Its real value comes from a monthly review, strong authentication, named ownership, and a rehearsed response—not from the existence of the page itself.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
Where is ChatGPT Security History?
On ChatGPT web, open Settings, choose Security and login, then select Security history. Availability can vary by account and rollout.
What does ChatGPT Security History show?
OpenAI says it includes recent sign-ins, sign-outs, and changes to MFA, passkeys, and other security settings, with time, device, and approximate location when available.
What should I do if I see an unfamiliar ChatGPT login?
Secure the linked email account, change the password from a trusted device, sign out other sessions, review MFA and passkeys, inspect connected services, rotate exposed API keys, and contact official support.
Does Security History replace an admin audit log?
No. It is an account-security view, not a complete inventory of workspace activity, connected apps, shared content, API credentials, or organizational audit events.
Tools mentioned in this article
ChatGPT
The general-purpose AI assistant that started it all
OpenAI's flagship conversational AI model, powering everything from casual chat to complex reasoning, coding, and creative work.
Read next