Anthropic’s Enterprise Frontier Safeguards Put Storage in Customer Control
Customer-controlled storage can narrow a privacy tradeoff, but buyers still need architecture, retention, alert, access, and incident evidence.
Bottom line
Anthropic’s Enterprise Frontier Safeguards combine customer-controlled data storage with misuse monitoring. The rollout is phased, and implementation details matter.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-30
Important limits
- • EFS was announced as a phased rollout; DiscoverAI has not validated a production deployment.
- • Architecture, eligibility, monitoring performance, and contract details may vary by customer and surface.
In this guide
Short answer
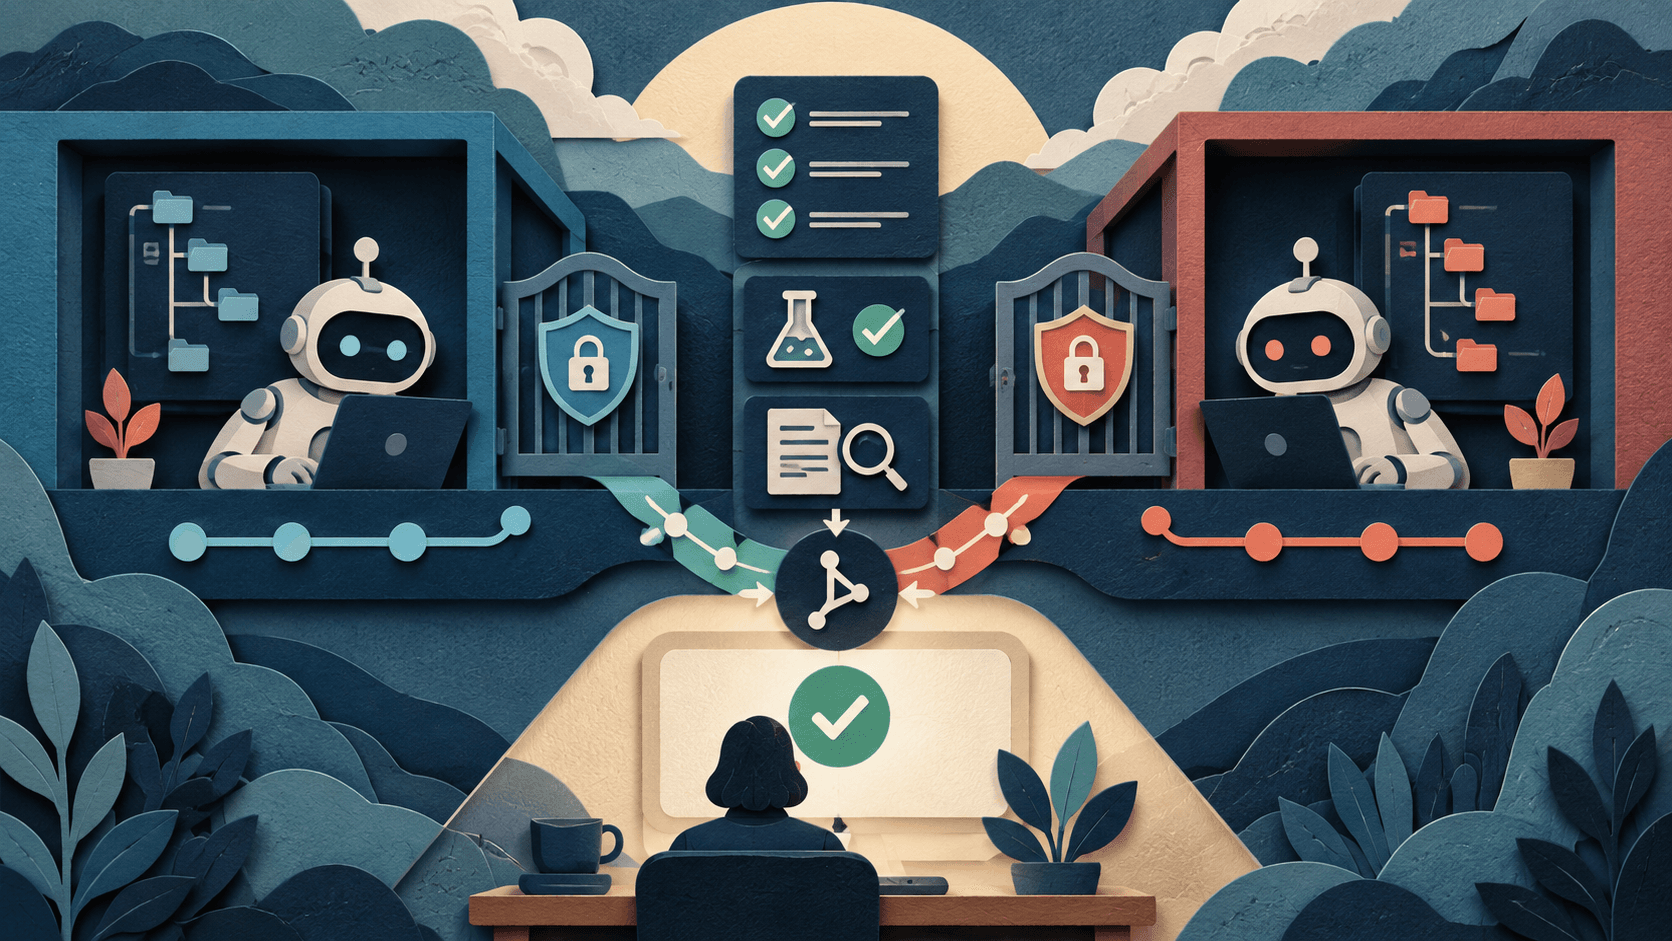
Anthropic announced Enterprise Frontier Safeguards, or EFS, on September 1, 2026. The planned service combines zero-data-retention privacy goals with safeguard monitoring while storing relevant customer data in cloud infrastructure controlled by the customer. Anthropic says rollout begins in phases later this fall for eligible enterprise customers. That is a design and availability commitment, not evidence from a completed deployment.
What problem EFS targets
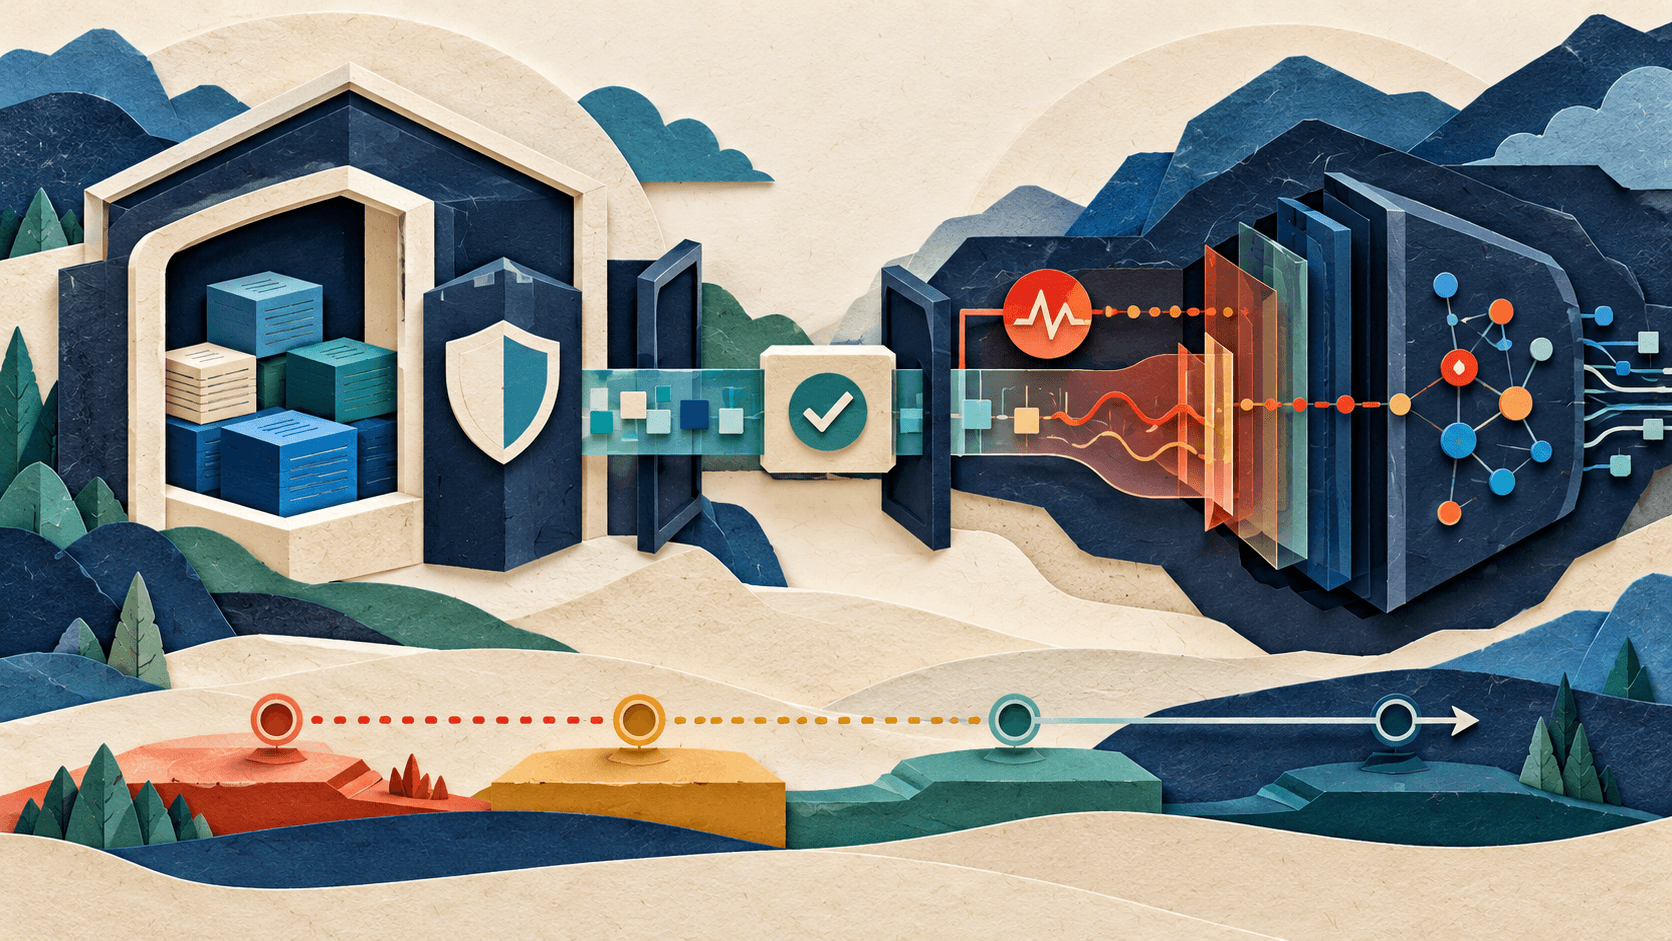
Some high-sensitivity customers want strong misuse safeguards without allowing a model provider to retain their prompts and outputs. Customer-controlled storage could let monitoring operate against data kept inside the customer's environment. The important questions are which data is inspected, where computation occurs, who can retrieve alerts, and what happens during an incident.
Availability is not uniform
Anthropic names Claude Code, Claude Enterprise, the Claude Platform, Amazon Bedrock, Claude Platform on AWS, Google's agent platform, and Microsoft Foundry as intended surfaces. Support, timing, configuration, and contractual terms may differ. Eligible customers are promised zero data retention on selected models during the transition.
Evidence buyers should request
Ask for architecture and data-flow diagrams; retention and deletion behavior; supported regions and services; encryption and key control; alert precision and latency; customer and provider access; failure modes; audit exports; incident escalation; false-positive handling; and proof that disabling or degrading monitoring fails visibly. Contract language should match the technical path.
Bottom line
EFS is a meaningful attempt to avoid framing privacy and safeguards as opposites. Procurement should remain conditional until the exact deployment path, controls, rollout state, and measured monitoring performance are documented for the customer's workload.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
What are Enterprise Frontier Safeguards?
Anthropic describes EFS as a way to combine misuse monitoring with customer-controlled cloud storage and zero-data-retention privacy goals.
Is EFS generally available?
No broad general availability was stated. Anthropic says rollout will occur in phases, beginning with eligible customers later in fall 2026.
Does customer-controlled storage mean Anthropic sees no data?
The announcement does not justify that blanket conclusion. Buyers need the exact monitoring, processing, alert, support, and incident-access data flow.
What should a security review request?
Request architecture, retention, encryption, access, alert, audit, failure, incident, regional, and contractual details for the exact deployment surface.
Tools mentioned in this article
Claude
Anthropic's thoughtful, safety-focused AI with exceptional long-form reasoning
Claude excels at deep analysis, long-form writing, and nuanced reasoning. Built by Anthropic with a focus on safety and helpfulness.
Read next