Google’s Gemini 3.8 Flash Cyber Finds and Patches Vulnerabilities—But Access Is Restricted
Google’s specialized security model is initially limited to vetted defenders, pairing lower-cost vulnerability research with identity, MFA, access-control, and use restrictions.
Bottom line
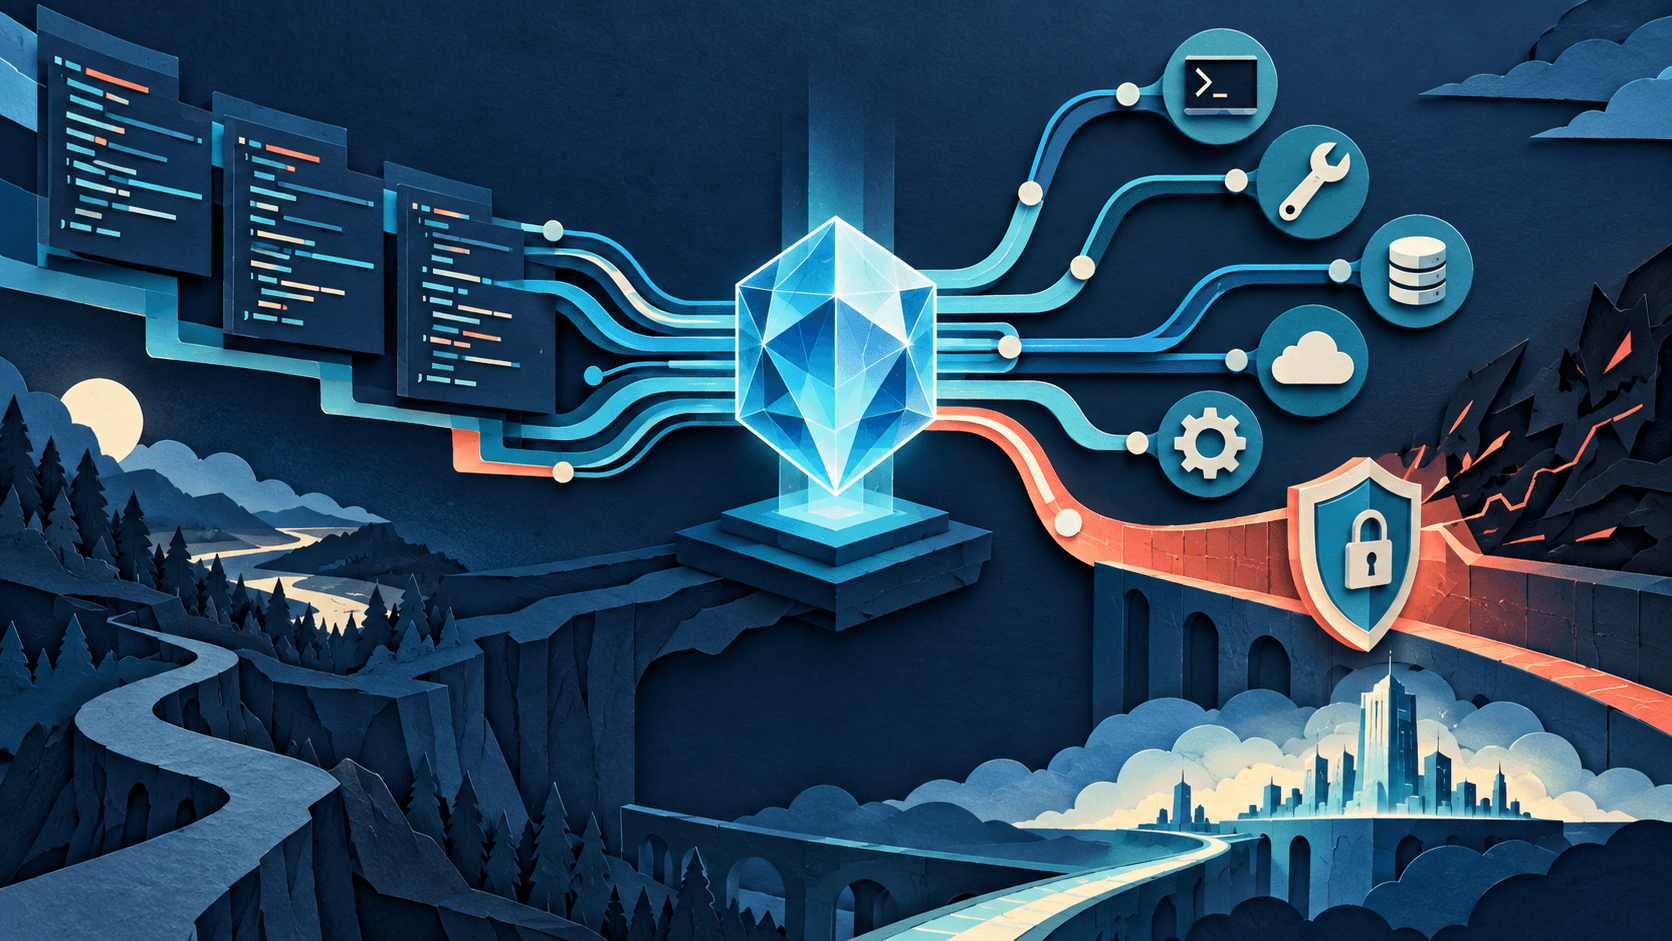
Gemini 3.8 Flash Cyber targets vulnerability discovery and automated patching, but only approved Fairwind partners get early access. Here is what the model and governance do—and do not prove.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-14
Important limits
- • Features, availability, and pricing can change after publication; confirm consequential details with the provider.
In this guide
*This research-based analysis covers Google's September 2026 Gemini 3.8 Flash Cyber and Fairwind Program materials. Benchmark and performance descriptions are Google-reported unless an external source is named; restricted access and program terms can change.*
The short answer
Google has introduced Gemini 3.8 Flash Cyber, a specialized model for autonomous vulnerability discovery and automated patching, through its restricted Fairwind Program. It is not a public security chatbot: Google says approved partners undergo due diligence and must limit access to authorized cybersecurity, incident-response, or penetration-testing teams.
Google reports 86.2% pass@1 on CyberGym, 71% on an internal vulnerability-discovery evaluation spanning 20 programming languages, and 47.2% on the external CWE-Bench patching benchmark. Those results make the model worth watching, but benchmark success does not establish that a generated finding is exploitable or that a patch is safe in a specific production system.
What does Gemini 3.8 Flash Cyber do?
Google positions the model to navigate complex codebases, locate hidden vulnerabilities, and generate fixes after discovery. Fairwind partners may also use it with CodeMender, Google's specialized code-security agent, so a workflow can move from a suspected weakness to a proposed patch and validation loop.
That workflow changes the review burden rather than removing it. Security teams still need to reproduce a finding, determine reachability and impact, inspect the patch, run unit and integration tests, check for regressions, and decide whether a change is safe to deploy. False positives consume scarce attention; false negatives create misplaced confidence.
Who can access it?
Early access is limited to approved Fairwind partners. Google says it performs organizational background checks, prohibits sharing or reselling access, and permits dual-use activity such as authorized threat simulation, reverse engineering, and malware analysis only for defensive or academic research.
Participating organizations must use user-level authentication, phishing-resistant multifactor authentication, applicable access controls, and employee-use tracking. Google says zero data retention is supported when the model is accessed directly as a managed model on Gemini Enterprise Agent Platform. Teams that are not eligible can use CodeMender with publicly available models, but do not receive the restricted Cyber model.
What do the benchmark results establish?
CyberGym and CWE-Bench provide repeatable comparisons for vulnerability discovery and patching. Google's internal multilingual-codebase test adds a broader, but vendor-controlled, signal. Together they suggest strong capability at Flash-style cost; they do not measure every language, dependency, build system, business-logic flaw, exploit chain, or production constraint.
The published 47.2% CWE-Bench pass@1 also makes the boundary visible: even on a defined benchmark, a first attempt often does not pass. Buyers should demand reproducible evidence for each finding and measure accepted fixes per dollar and reviewer hour, not the number of issues a model can generate.
What should defenders test before trusting it?
Run the model against repositories and deliberately seeded vulnerabilities whose answers are known. Track confirmed true positives, severity accuracy, duplicates, missed flaws, time to reproduce, patch acceptance, test pass rates, regressions, cost, and reviewer time. Include prompt injection inside issues, comments, documentation, dependencies, and web pages an agent may inspect.
Keep credentials isolated, repositories scoped, outbound access controlled, and deployment separate from patch generation. Require human approval for changes and preserve full action logs. The restricted program's identity and access rules are useful, but each customer still owns authorization boundaries inside its environment.
The verdict
Gemini 3.8 Flash Cyber is notable both for its security capability and for Google's decision to restrict distribution through a vetted defender program. The combination acknowledges that a model able to find and patch vulnerabilities also carries obvious dual-use risk.
The right use is a governed force multiplier for qualified defenders—not an autonomous permission to scan, change, or deploy. Benchmark leadership is not workload proof; reproducible findings, safe patches, bounded access, and human accountability remain the standard.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
What is Gemini 3.8 Flash Cyber?
It is Google's specialized cybersecurity model for vulnerability discovery and automated patching, initially available to approved defenders through the Fairwind Program.
Can anyone access Gemini 3.8 Flash Cyber?
No. Google says Fairwind access is restricted to vetted partners, with due diligence, user-level identity, phishing-resistant MFA, access controls, use tracking, and limits on redistribution.
How well does Gemini 3.8 Flash Cyber perform?
Google reports 86.2% pass@1 on CyberGym, 71% on an internal 20-language vulnerability test, and 47.2% on CWE-Bench. These results do not replace validation on a buyer's own code.
Does Gemini 3.8 Flash Cyber support zero data retention?
Google says zero data retention is supported when Fairwind partners access it directly as a managed model on Gemini Enterprise Agent Platform.
Found this useful?
Get the next one in your inbox.
One five-minute briefing a week: a meaningful change, a practical workflow, and a clearer tool decision—already filtered for lean teams.
Free · one email a week · unsubscribe any time
Tools mentioned in this article
Google Gemini
Google's deeply integrated AI assistant with unmatched access to Google's ecosystem
Gemini combines powerful AI with Google's vast data ecosystem — Search, Gmail, Docs, YouTube, and more — for a uniquely integrated experience.
Read next
Recommended for you
TypingMind Review 2026: Multi-Model Chat, Pricing, and Privacy
A research-based TypingMind review covering capabilities, pricing, privacy, limitations, and a fair buyer test.
TypingMind unifies multiple AI APIs in a local-first interface, but API spend, browser storage, optional cloud services, and provider policies determine its real value and privacy.
Read guide
Dia Browser Review 2026: Is the AI Browser Worth Switching To?
Looker Studio vs Power BI for AI Analytics Workflows in 2026
Gamma AI Review 2026: Fast Presentations, but Is It Worth Paying For?