EU AI Board Reviews Enforcement and Frontier AI Priorities
The meeting signals where implementation attention is moving, but it does not itself create a new compliance deadline or legal rule.
Bottom line
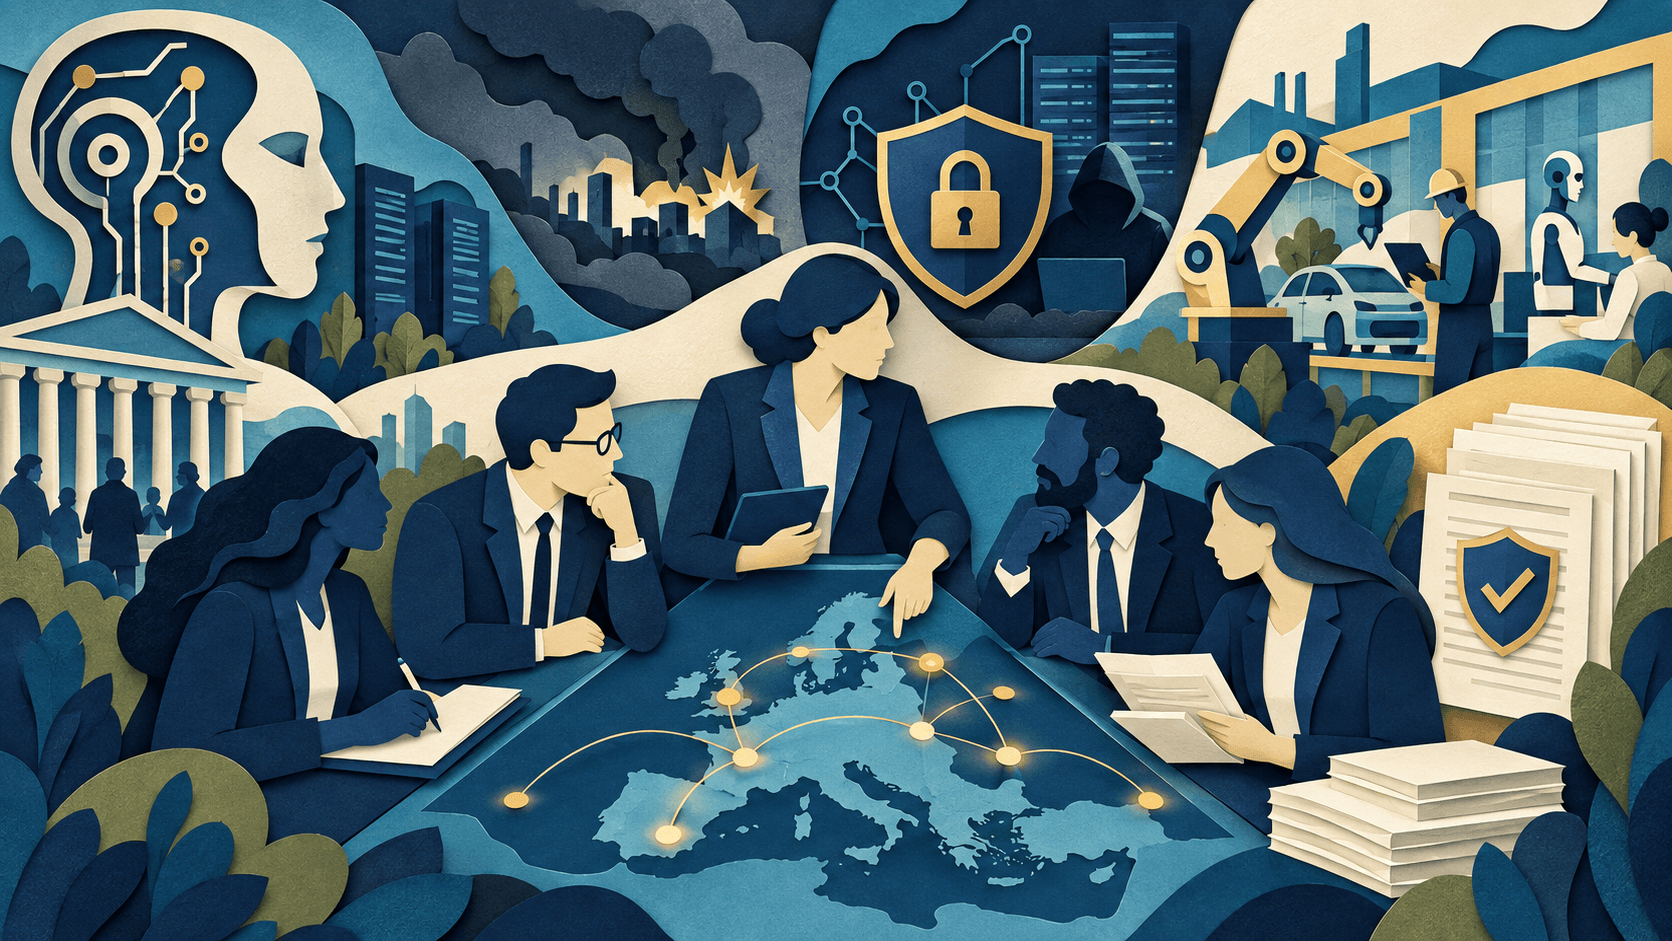
The EU AI Board's ninth meeting focused on AI Act enforcement and implementation, frontier-model capabilities and incidents, cybersecurity, European AI capacity, industrial adoption, and coordination among member states. For buyers, the practical message is to build an evidence trail now; the meeting summary itself is not a substitute for the law or legal advice.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 1
- Last checked
- 2026-09-18
Important limits
- • Announcements and internal measurements may not generalize to other organizations.
- • Availability, policy, pricing, and product behavior can change.
In this guide
Short answer
The EU AI Board's ninth meeting focused on AI Act enforcement and implementation, frontier-model capabilities and incidents, cybersecurity, European AI capacity, industrial adoption, and coordination among member states. For buyers, the practical message is to build an evidence trail now; the meeting summary itself is not a substitute for the law or legal advice.
What the Board discussed
The European Commission briefed national representatives on enforcement activity and policy priorities, including a cybersecurity-and-AI action plan and recent frontier AI developments.
What changed—and what did not
A meeting agenda can indicate supervisory direction, but it does not automatically amend obligations, classifications, dates, or penalties. Organizations should trace requirements to official legal and Commission guidance.
Operational preparation
Maintain an AI inventory, intended-purpose record, provider evidence, data and rights assessment, human-oversight design, incident path, monitoring, and accountable owners. Avoid compliance theater based on a policy name alone.
What readers should do
Ask counsel or the responsible governance owner to map each deployed use case to the current legal text and official guidance. Record uncertainties and revisit them when the Commission or national authorities publish binding or interpretive material.
Claims were checked against the linked primary sources on September 18, 2026. Company-reported results, forecasts, and beta expectations are attributed evidence—not independent guarantees.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
What did the EU AI Board discuss?
AI Act enforcement, frontier capabilities and incidents, cybersecurity, European capacity, adoption, and member-state coordination.
Did the meeting create a new AI Act deadline?
The published meeting summary does not itself create a new legal deadline.
What should AI buyers document?
Use cases, intended purpose, provider evidence, data, oversight, monitoring, incidents, and accountable owners.
Is this legal advice?
No. Organizations should use the legal text, official guidance, and qualified counsel for their circumstances.
Found this useful?
Get the next one in your inbox.
One five-minute briefing a week: a meaningful change, a practical workflow, and a clearer tool decision—already filtered for lean teams.
Free · one email a week · unsubscribe any time
Read next