Build an AI Access Inventory Before Connecting Work Apps
A one-page access map turns vague AI permission reviews into an owned, testable control before data and actions spread across assistants.
Bottom line
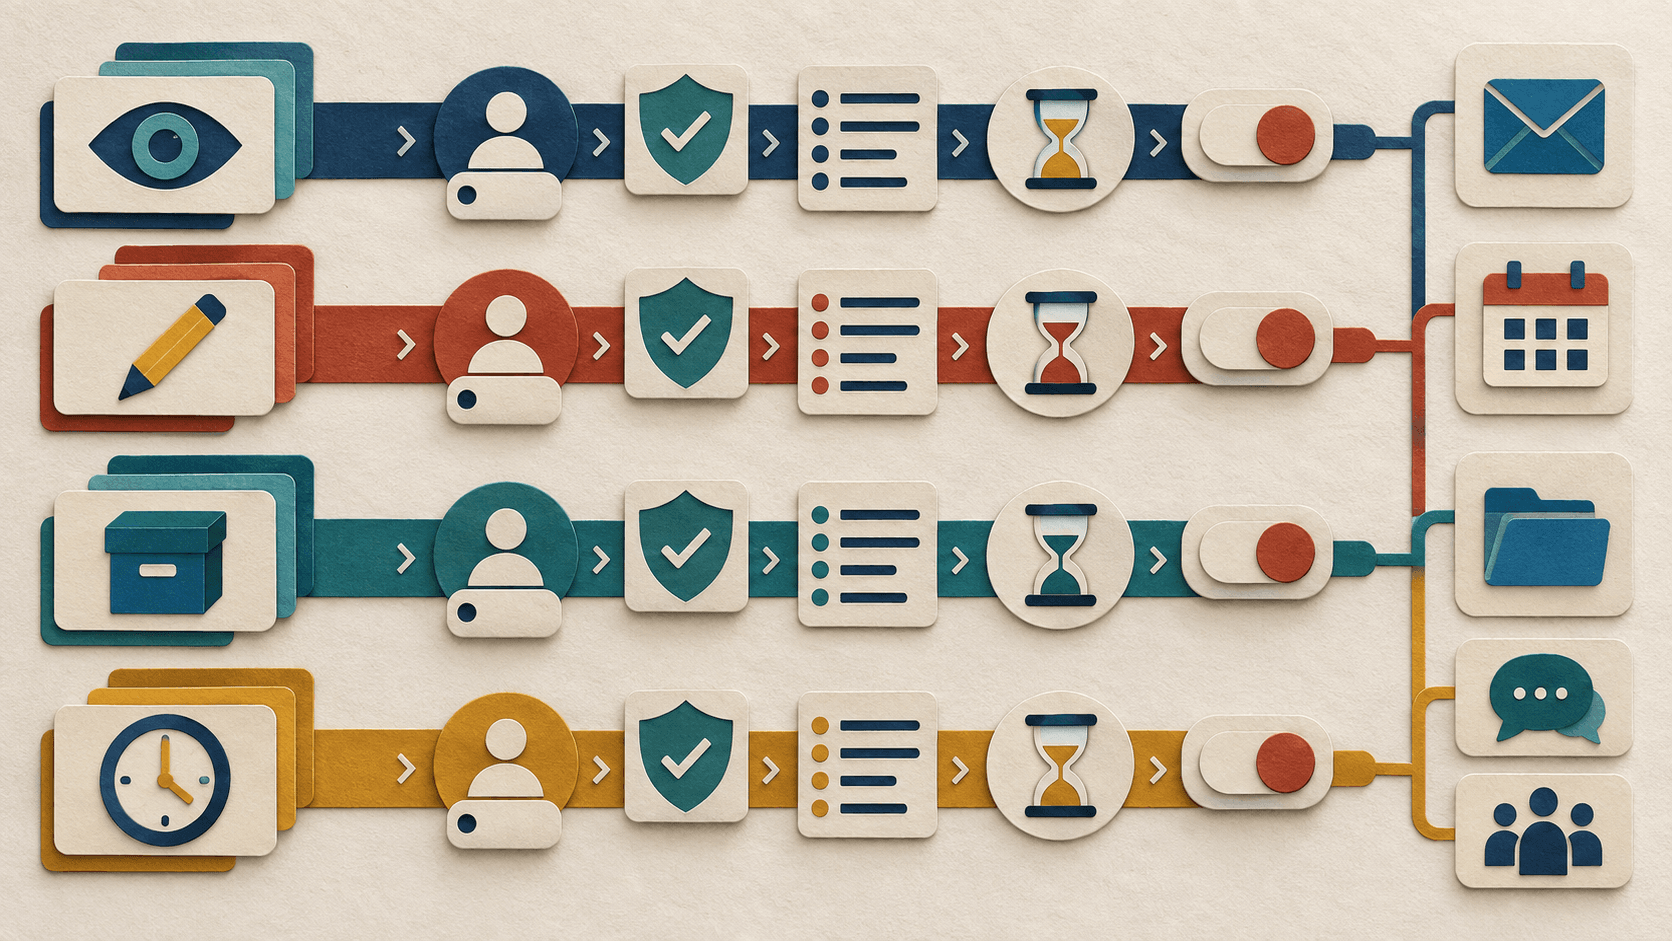
Document each AI tool's identities, data sources, write actions, retention, triggers, approvals, logs, and revocation path before production access.
Editorial accountability
Who checked this guide
- Evaluation type
- Research-based verification
- Last materially checked
- Evidence
- 4 listed sources
Hands-on testing is identified explicitly. Research-based coverage uses cited product documentation and other named sources; it does not imply every paid plan was used. Read the full methodology.
Editorial basis
What this guidance is based on
- Editorial basis
- Source-led analysis
- Primary references
- 4
- Products covered
- 3
- Last checked
- 2026-09-22
Important limits
- • The template is not a substitute for legal, privacy, security, or records advice.
- • Required controls depend on jurisdiction, industry, data, and action consequence.
In this guide
Short answer
Before connecting an AI assistant to work apps, create an access inventory that answers four verbs: what can it read, what can it write, what does it retain, and what can trigger it? Add the acting identity, owner, approvals, logs, expiry, and revocation test. This small control catches dangerous ambiguity that a generic vendor checklist misses.
1. Inventory identities and owners
Record the business owner, technical owner, vendor, workspace, service account, delegated user, administrator, model providers, and subprocessors. Distinguish the person authorizing access from the identity used at runtime. No production connection should be ownerless.
2. Map read scope
List every mailbox, calendar, drive, chat, CRM object, repository, database, website, and uploaded file. Record whether source permissions are enforced at query time, whether shared links or overshared folders expand access, and whether indexing creates another stored copy.
3. Map write and action scope
Separate drafts from sends, suggestions from edits, and prepared transactions from committed ones. Name every action: send email, invite attendees, update CRM, publish content, change permissions, purchase, refund, delete, or run code. Require explicit approval for consequential or irreversible actions and test denial paths.
4. Record retention and learning
Document prompts, outputs, transcripts, indexes, embeddings, memory, logs, feedback, cache duration, backups, training use, deletion timing, exports, and legal holds. “We do not train on your data” does not answer retention, human access, subprocessors, or deletion.
5. Record triggers and boundaries
Identify whether runs start from a person, schedule, webhook, new message, changed record, or another agent. State input validation, duplicate prevention, rate and spend caps, allowed hours, escalation, degraded mode, and the maximum action count per run.
6. Test revocation
Disconnect the integration, revoke tokens, remove a user, reduce source permissions, disable a workflow, and confirm that reads, writes, schedules, caches, and background runs stop. Capture evidence and repeat quarterly or after a material product change.
A compact inventory template
Use these columns: tool; owner; runtime identity; sources read; data copied or indexed; writes/actions; triggers; approval; retention/deletion; model/subprocessors; logs/alerts; spend cap; expiry; revocation result; last review; next review.
Bottom line
The inventory is not bureaucracy for its own sake. It makes access visible enough to minimize, test, revoke, and explain—before an assistant quietly becomes part of the control plane for everyday work.
Sources and verification
Product details and claims were checked against the following primary sources.
Frequently asked questions
What is an AI access inventory?
It is a living record of each AI system's owner, identity, readable data, write actions, retention, triggers, approvals, logs, expiry, and revocation evidence.
How is it different from an app list?
An app list names products; an access inventory maps actual identities, data flows, actions, storage, automation triggers, and controls for each deployment.
How often should it be reviewed?
Review it at least quarterly and whenever permissions, connectors, models, subprocessors, retention, automation, ownership, or business purpose changes.
What should teams test first?
Test least-privilege access, denied actions, participant notice, duplicate prevention, deletion, token revocation, user removal, workflow shutdown, logs, alerts, and rollback.
Found this useful?
Get the next one in your inbox.
One five-minute briefing a week: a meaningful change, a practical workflow, and a clearer tool decision—already filtered for lean teams.
Free · one email a week · unsubscribe any time
Recommended tool
Use HyperWrite if this workflow fits your team
HyperWrite is worth a trial for people who want writing and research help across the browser rather than in one isolated editor. Its broad context is also the main risk: verify what the extension can access, require review before external actions, and judge value by accepted drafts and sourced research—not generation volume.
Tools mentioned in this article
HyperWrite
HyperWrite combines AI writing, rewriting, research, personalization, and a Chrome extension that can assist inside websites where users already work
HyperWrite combines AI writing, rewriting, research, personalization, and a Chrome extension that can assist inside websites where users already work.
Zapier AI
A practical AI tool for productivity workflows
Zapier AI helps professionals improve productivity workflows with AI-assisted drafting, automation, analysis, or production features.
Read next